

- Identification between installed Maia runners and your Maia account.
- Storing database credentials to be used when configuring a pipeline’s source.
- Storing source credentials for use in connectors.
Secret manager flow in Maia
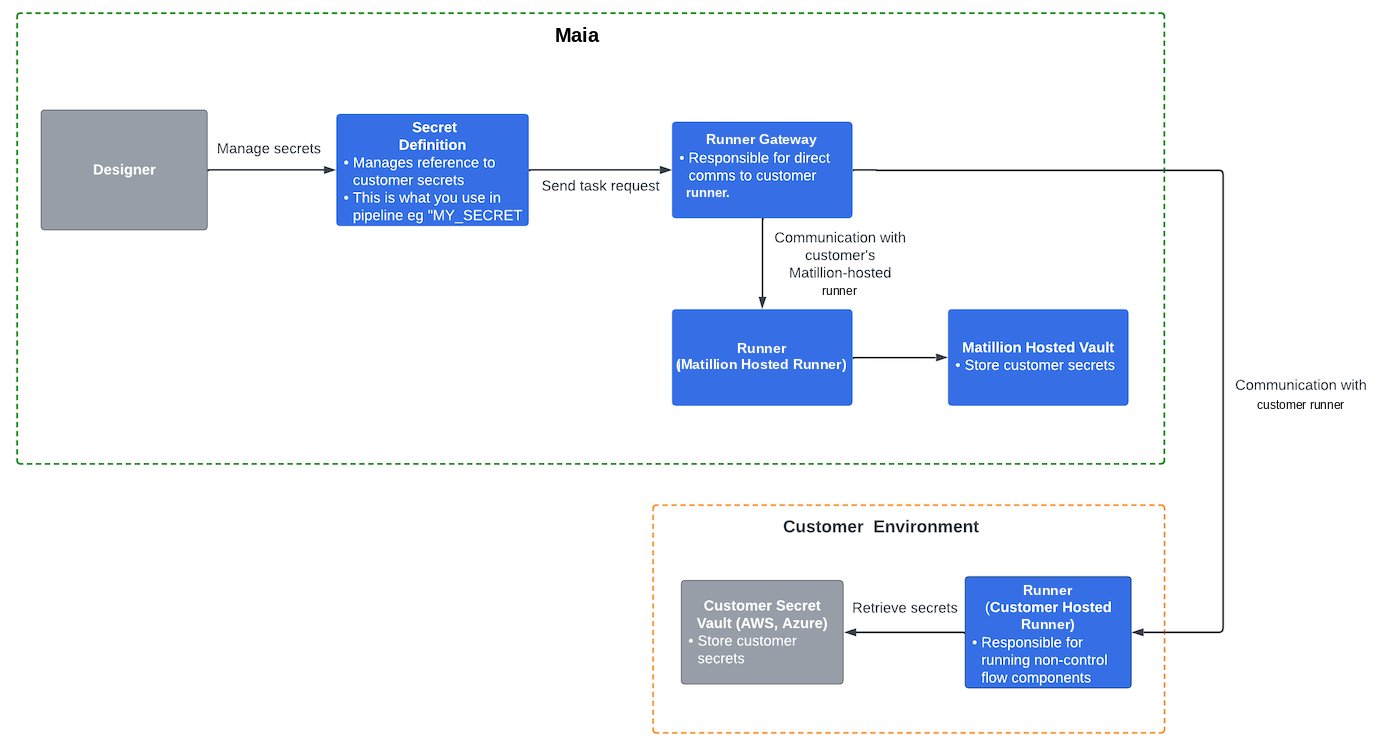
- Users authenticate themselves to access Maia—where secrets, including customer references, are managed securely.
- Users invoke Designer to create and configure data pipelines and to define secrets for an existing cloud provider’s secret within the corresponding secret definition.
- Task requests are sent to the Runner Gateway for direct communication with customer-hosted Maia runners, and the scheduler coordinates pipeline executions based on schedules and triggers.
- A Matillion-hosted Maia runner securely stores and retrieves customer secrets from the Matillion-hosted vault as necessary for pipeline execution.
- Customer secret vaults securely store and retrieve customer secrets. A customer-hosted Maia runner provides the option to execute data pipelines on-premises or in the customer’s cloud network.
Security benefits
- Maia deployed as Hybrid SaaS never directly stores passwords or keys, relying instead on your cloud provider for secure storage.
- Your cloud provider’s secret manager offers robust security measures for protecting credentials, ensuring the confidentiality and integrity of sensitive information.
Runners
The Maia runner is responsible for processing pipeline tasks, which are individual units of work within a data integration workflow. These tasks handle data integration and transformation operations by securely connecting to data sources and targets. The Maia runner can be configured in two ways:- Full SaaS: Fully managed by Matillion and resides in Matillion’s VPC.
- Hybrid SaaS: Runs inside a user’s VPC.
Maia runners can access stored secrets, which serve as the repository for all your secrets. In your projects, information is limited to the names of Maia runners and the secrets they can access. Maia doesn’t provide direct access to the values of secrets. However, these secrets can be used within your projects to access your data services.
Using secrets
In Maia, secrets and secret definitions are scoped to be used by a specific Maia runner. A secret can be used by multiple connections and projects that are linked to that Maia runner. To use a secret in Maia:- Create a named secret in your cloud provider’s secret manager.
- Add a connection in Maia and point the connection at your named secret.
If you need to store multiple passwords and keys, each should be in a separate, named secret.